Project
1. Purpose and Scope
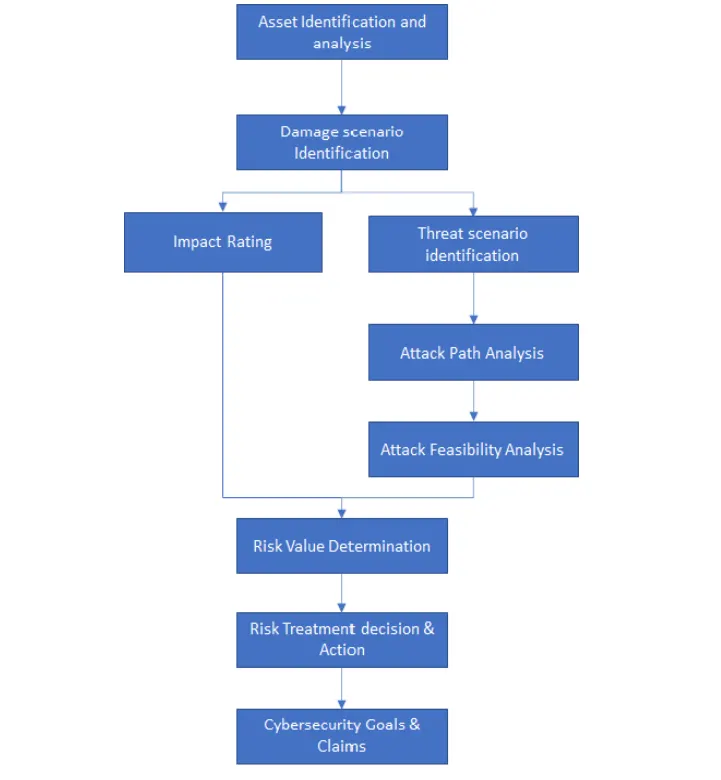
The document's purpose is to outline the standards for threat analysis and risk assessment for the declaration of a car's headlamp system. All cybersecurity-related initiatives that include threat analysis and risk assessment are covered under the scope of this guideline.
2. Process Flow
3. Item definition
A headlights is a lamp that is mounted on the front of a car to light the way. Although headlights and headlamps are frequently used interchangeably, in the most formal sense, headlight refers to the gadget's beam of light and headlamp to the device itself. Daytime Exercise With lights, front-end collisions are less likely, and accidents during the day are greatly reduced. These lights are always on when the engine is operating, day or night. They are positioned in the car's front bumper or are built into the headlights and are very dim.
BCM Unit: Meet Body Control Module (BCM), the brain behind Automotive Electronics. It controls the inter-ECU communication for a variety of body electronics systems, including power windows, wipers, automatic door locks, HVAC, headlamps, and rear lamps (automotive lighting).
Through early design testing of probable edge situations and validation of control law behaviour, Modern Headlamp has accelerated up the development of intelligent headlights. Real-time optical simulation in a simulated driving environment makes it simple to evaluate creative and intelligent light beams. Enhance the quality of your finished work while drastically lowering the possibility of discovering problems after the fact.
4. Asset Identification
[As.1] There is a CAN message for lamp ON/OFF request, in such as case CAN frame will be an asset
[As.2] Power distribution box provide power to the headlamp, so PDB is one of the asset for car headlamp
[As.3] Genivi – a standard for Linux based systems used for in-car infotainment systems. for example, a cable would run from the battery to a switch and on to the headlights.
5. Threat Scenarios identification
Name of Threat scenario: spoofing on CAN Bus
Cause of compromise: TC.1: spoofing
Acts on: CAN Bus
Compromises: Confidentiality, I: Integrity
Threatens: +
Attack Tree: AS.1
Realizes: DS.1: Headlamp turns off unexpectedly
DS.2: Headlamp turns on unexpectedly
Damped by: A.1
Name of Threat scenario: Tampering on CAN Message
Cause of compromise: TC.2: Tampering
Acts on: CAN Bus
Compromises: Confidentiality, I: Integrity
Threatens: +
Attack Tree: AS.2
Realizes: DS.1: Headlamp brightness increases suddenly
DS.2: Headlamp changes its focus randomly
Damped by: A.2
6. Impact Analysis
The impact of the damage scenarios on the stakeholders will be evaluated. The following impact categories on road users will be examined.
1. Safety
2. Financial
3. Operational
4. Privacy
Depending on the stakeholders, it may be possible to identify effect categories other than S, F, O, and P. The damage scenario's impact rating must fall within one of the following categories: - Major, - Moderate, - Negligible, or - Severe The classification of hazardous occurrences in ISO 26262-3:2018, 6.4.3, shall be used to determine implications on safety.
Name of Threat scenario: spoofing on CAN Bus [TS.1]
Impact Analysis for spoofing on CAN Bus
|
Impact Rating |
Criteria for Safety Impact Rating |
|
Major |
S2: Severe and life-threatening injuries (survival probable) |
Table 1: Safety impact rating criteria
|
Moderate |
The financial harm has unfavourable effects that the stakeholder who is harmed can manage with their limited means. |
Table 2: Financial impact rating criteria
|
Impact Rating |
Criteria for Operational Impact Rating |
|
Moderate |
A vehicle's performance or function is partially degraded as a result of the operational damage. |
Table 3: Operational impact rating criteria
|
Impact Rating |
Criteria for Privacy Impact Rating |
|
Negligible |
Damage to privacy has little impact or may only cause minor annoyance to other road users. The information pertaining to the road user in this instance is not sensitive and is difficult to connect to a PII principle. |
Table 4: Privacy impact rating criteria
Table 5: Computation of impact rating value
|
Safety impact rating criteria |
Financial impact rating criteria |
Operational impact rating criteria |
Computation of impact ratting |
|
|
Impact |
||||
|
Negligible |
0 |
0 |
0 |
0 |
|
moderate |
10 |
1 |
1 |
1 |
|
major |
100 |
10 |
10 |
10 |
|
severe |
1000 |
100 |
100 |
100 |
Name of Threat scenario: Tampering on CAN Message
Impact Analysis for Tampering on CAN Message [TS.2]
|
Impact Rating |
Criteria for Safety Impact Rating |
|
Major |
S2: Severe and life-threatening injuries (survival probable) |
Table 1: Safety impact rating criteria
|
Moderate |
The financial harm has unfavourable effects that the stakeholder who is harmed can manage with their limited means. |
Table 2: Financial impact rating criteria
|
Impact Rating |
Criteria for Operational Impact Rating |
|
Moderate |
A vehicle's performance or function is partially degraded as a result of the operational damage. |
Table 3: Operational impact rating criteria
|
Impact Rating |
Criteria for Privacy Impact Rating |
|
Negligible |
Damage to privacy has little impact or may only cause minor annoyance to other road users. The information pertaining to the road user in this instance is not sensitive and is difficult to connect to a PII principle. |
Table 4: Privacy impact rating criteria
Table 5: Computation of impact rating value
|
Safety impact rating criteria |
Financial impact rating criteria |
Operational impact rating criteria |
Computation of impact ratting |
|
|
Impact |
||||
|
Negligible |
0 |
0 |
0 |
0 |
|
moderate |
10 |
1 |
1 |
1 |
|
major |
100 |
10 |
10 |
10 |
|
severe |
1000 |
100 |
100 |
100 |
7.Attack paths analysis
-
using the OBD cable for on-board diagnostics. Below the dashboard, you can see the 16-pin connector and the OBD connector. This may be connected to any laptop or ECU to begin sniffing all CAN communications.
-
Locate the CAN bus within the vehicle. Twisted pair cables, CAN high and CAN low, make up the CAN bus. There is also a ground connection present in addition to this. After connecting these three wires to the ECU, you may begin sniffing any CAN communications.
8. Attack paths feasibility
Attack vector-based approach
When using an attack vector-based strategy, it is important to assess the main attack vector (CVSS) of the assault path. The greater the assault feasibility grade, the farther away (both physically and intellectually) an attacker must be to use the attack path. The underlying premise is that more prospective attackers can use the internet to exploit a vulnerability than they can use an attack method that necessitates physical access to the object or component.
spoofing on CAN Bus
|
Attack Feasibility Rating |
Determination Criteria |
|
Very low |
Physical: Threat agents require physical access to realize the attack path. |
Tampering on CAN Bus
|
Attack Feasibility Rating |
Determination Criteria |
|
Very low |
Physical: Threat agents require physical access to realize the attack path. |
9.Risk Value Determination
Value [Risk] = Impact x Feasibility [Attack path]
10. Risk treatment decision
R1: Denial of Service on Gateway ECU, Whitelist of CAN Messages | none | treated via AV: Avoidance | rationale considered impossible
R2: Spoofing of CAN Bus | 1 | treated via R:Reduction | rationale mitigated by controls
R3:Tampering on Gateway Ecu,Whitelist of CAN messages | none | treated via R:Reduction | rationale Dumped by assumption