Project 2 - Installing BWAPP – web app on your local machine
1.
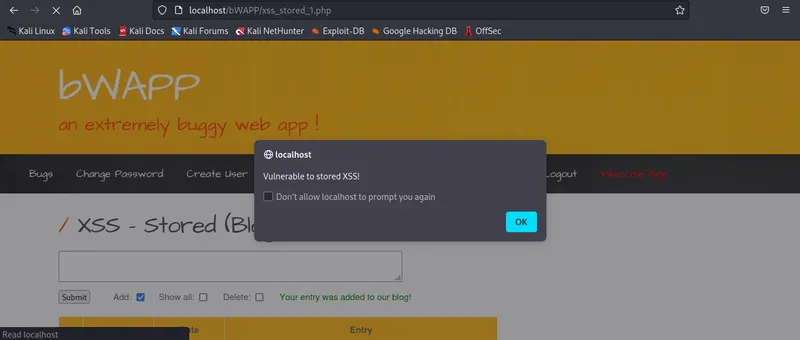
- Cross-Site Scripting - Stored (Blog):
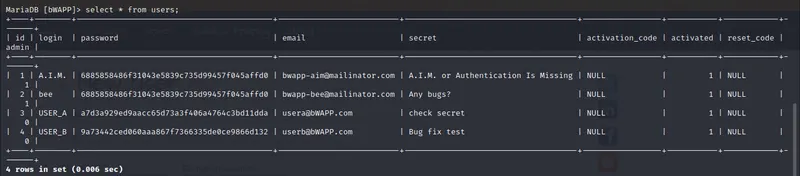
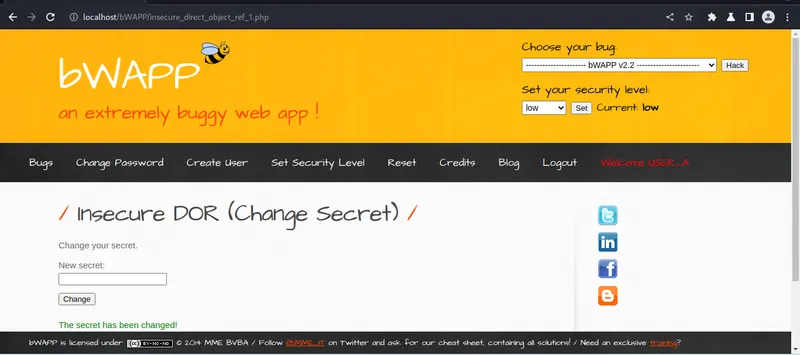
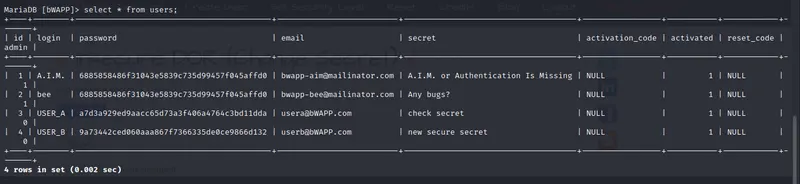
- Insecure DOR (Change Secret) – Create 2 users. Login as user A and try to change the password (secret) of user B.
Created 2 users: USER_A and USER_B
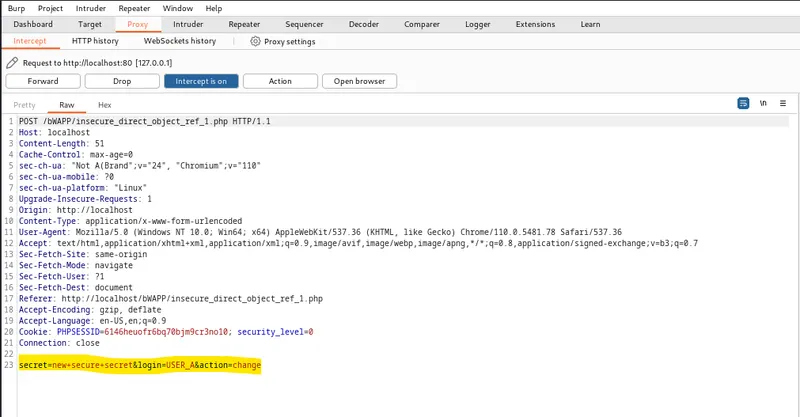
Next step, have changed the login=USER_B in the request and forwarded to change the secret=new secure secret
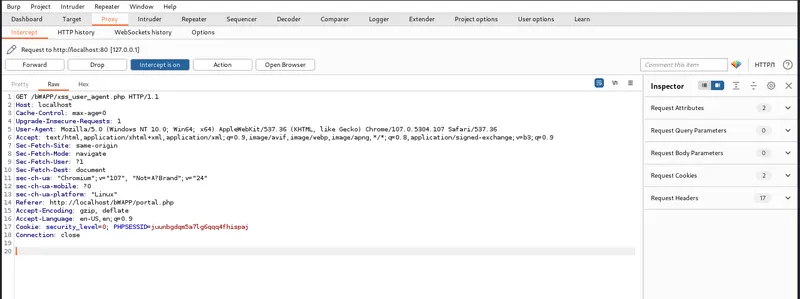
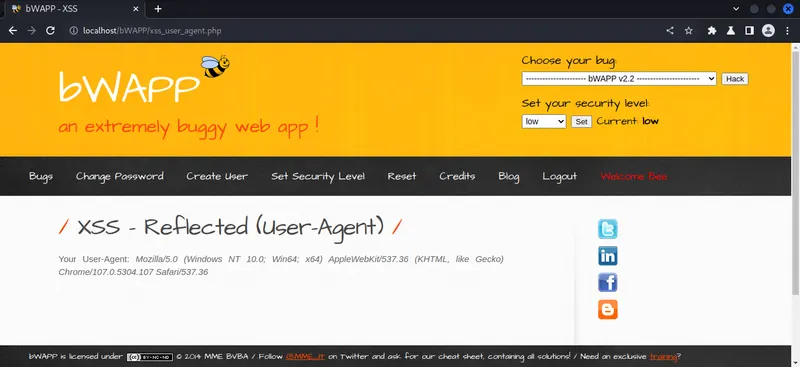
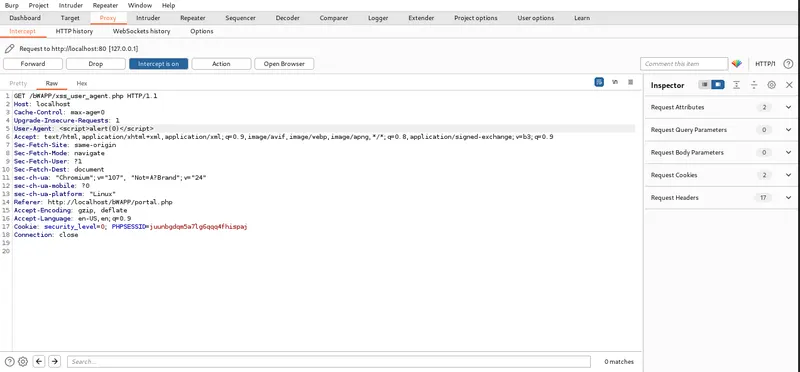
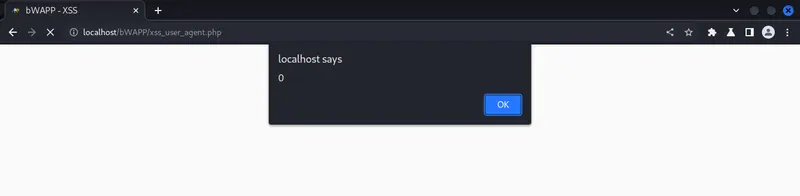
- Cross-Site Scripting - Reflected (User-Agent) – Inject malicious script and exploit Reflected XSS on the ‘user-agent’ request header. The malicious script should trigger an alert pop-up with number ‘0’.
2.
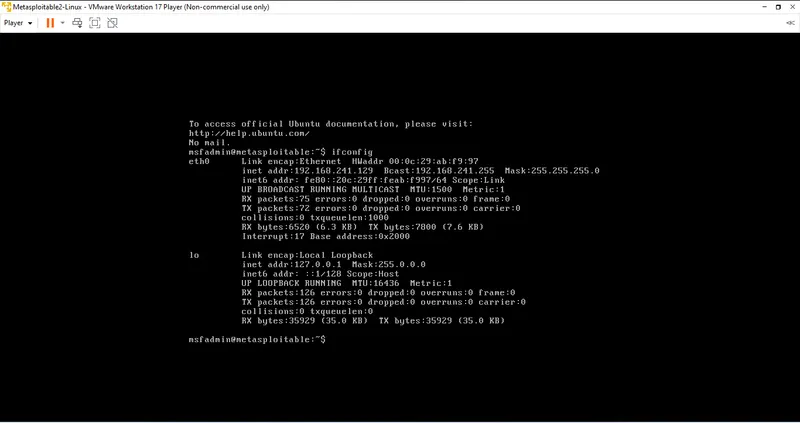
IP Address of the Metasploitable2 machine after successful boot up:
192.168.241.129
After downloading Nessus Community Edition,
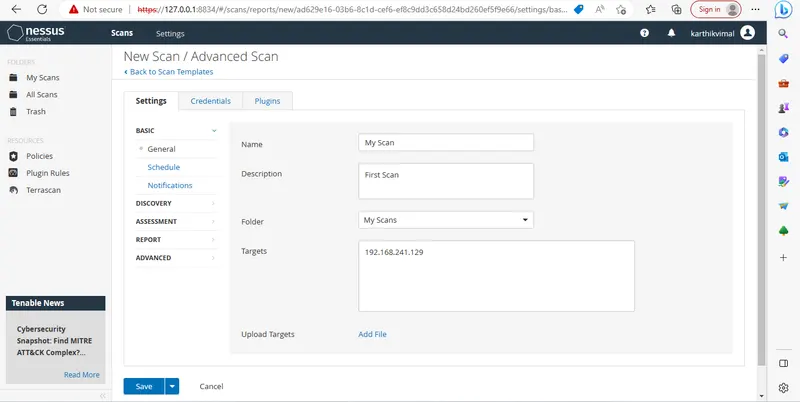
An advanced scan is started for the target IP Address of Metasploitable2 running on VM.
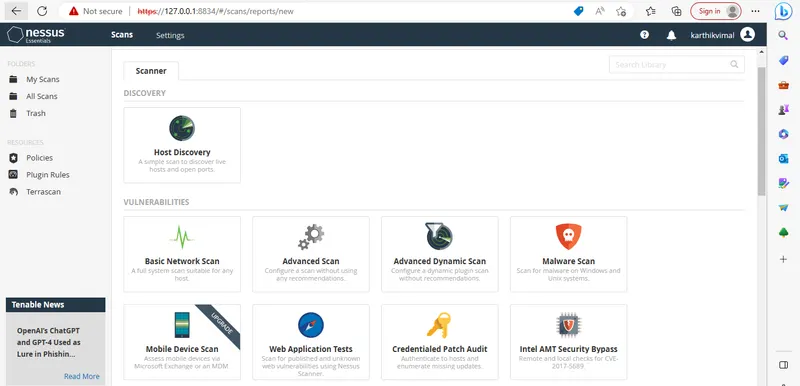
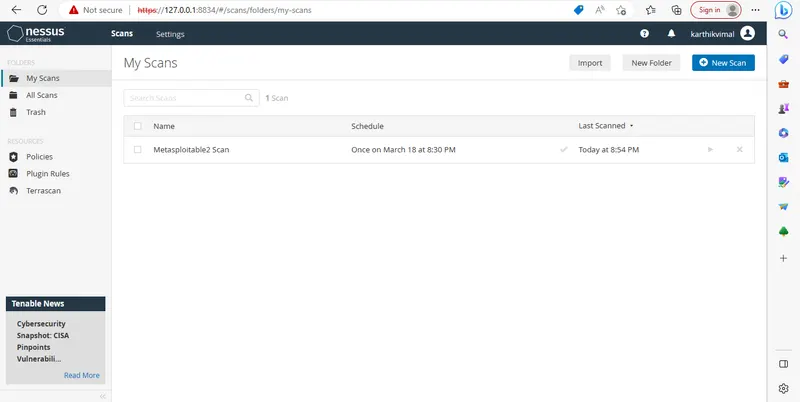
Scan started with providing IP details and configurations.
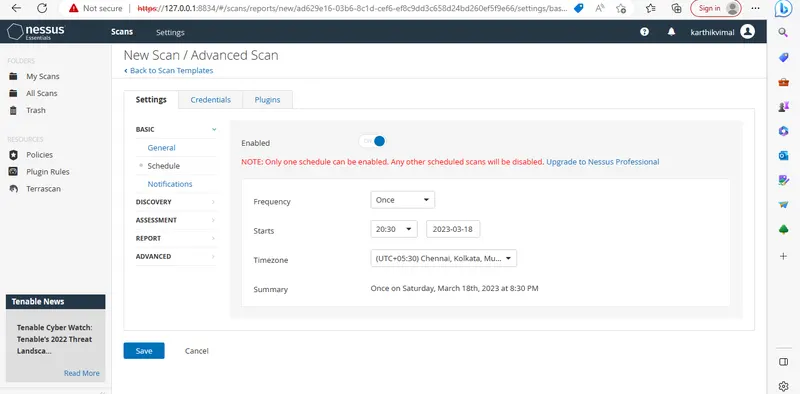
Change settings to schedule the scan to be taken in a particular time:
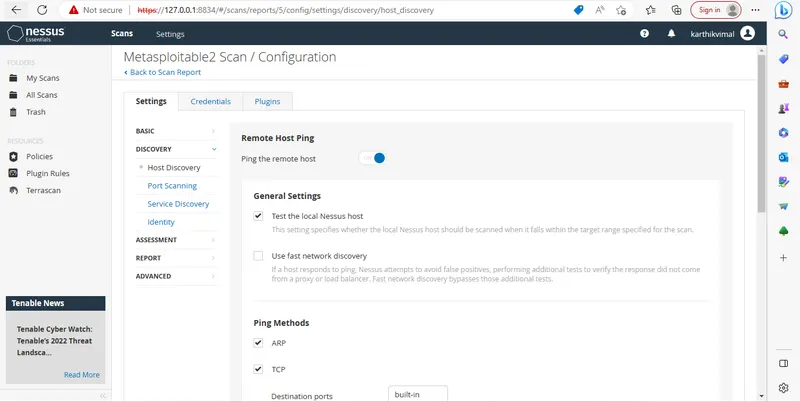
Adjust the Host configuration, Ping methods for the target IP with the TCP ports,ARP Protocols:
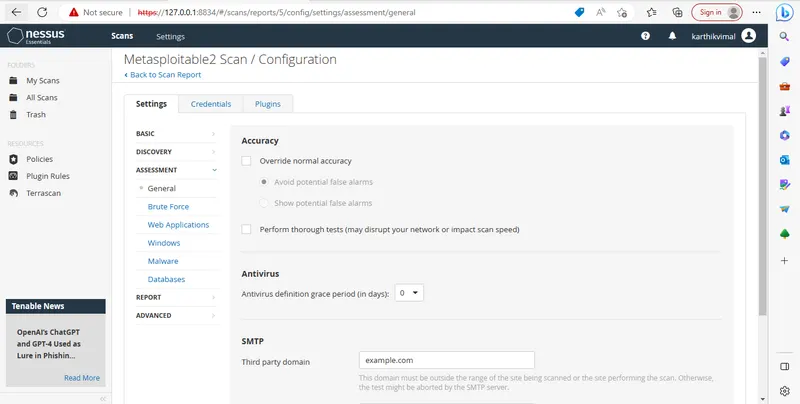
The next step provides the details for Discovery scanning configurations such as malwares, databases,brute force ,applications from HOST to check the vulnerability ports . This is used to find the efficient rates of the target IP:
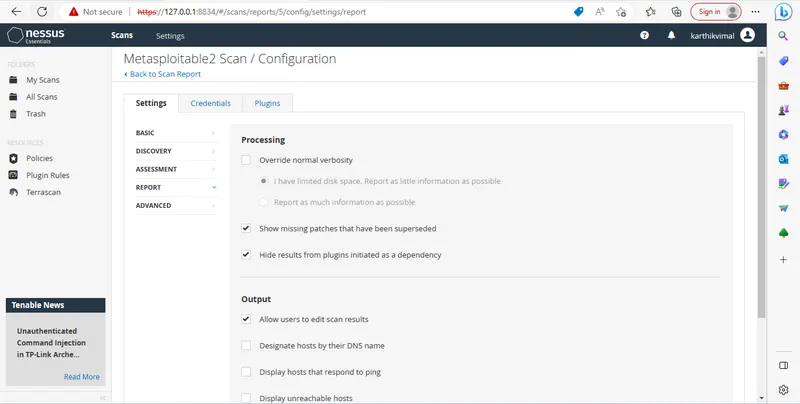
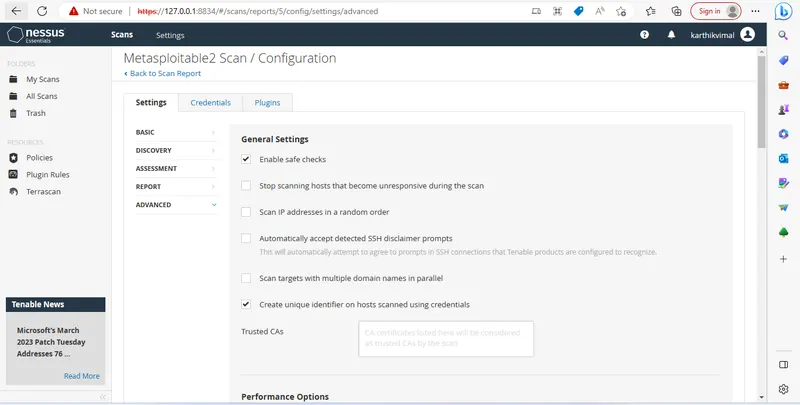
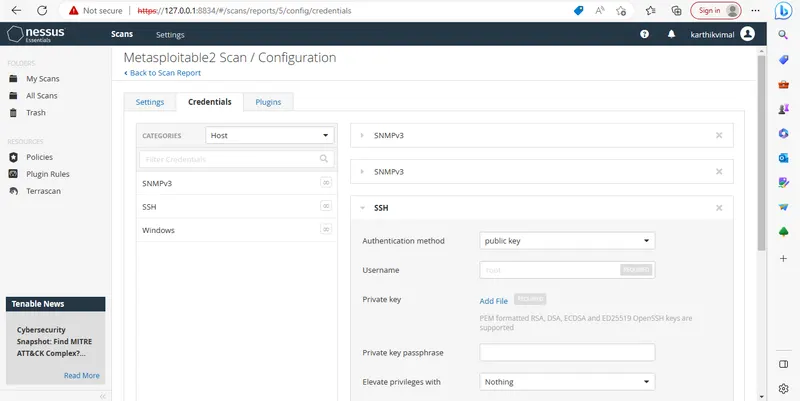
In the credentials part, it is used to identify the robustness and checks the OS authentication such as Windows, Unix - linux,fedora, redhat, debian etc. SSH - linux, Windows - Servers, Windows OS.
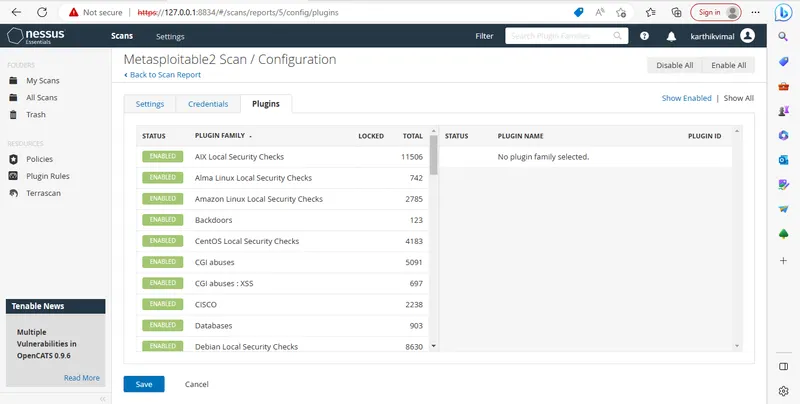
In Plugins, disable the not required parts from the target systems or we can enable all the plugins to validate the known vulnerabilities of the target OS. Once the details given in plugins to check, it will report and log the data in the report for each vulnerable feeds. Should keep licensed software to get the accurate scans to view the vulnerability rate in the systems if not the scans will not detect the corrupted plugins or threats.
After the vulnerability check, the report is downloaded from the options provided which gives all the information regarding the vulnerability scan for the target IP address.
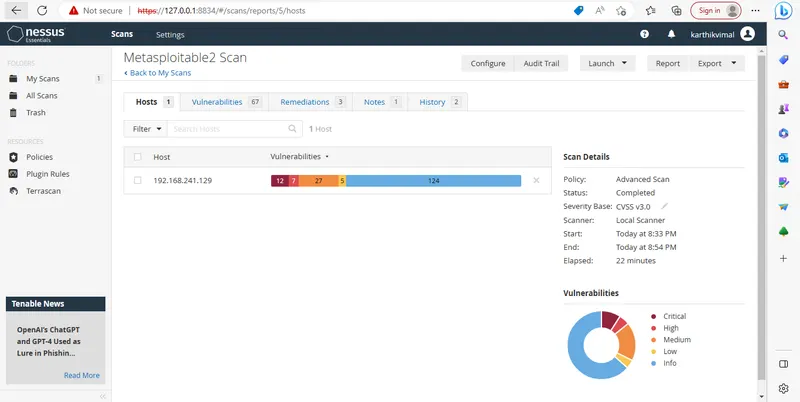
The vulnerability and full report has been generated for the target IP Address and attached for reference.